Cyberwise · Your Compliance Partner
Strengthen your
cybersecurity.Take control of your
compliance.
Cyberwise combines technical security assessments with governance and compliance expertise. We turn findings into clear priorities, guide the improvements and check that measures actually work.
01Positioning
From compliance requirements to cybersecurity that works.
We go beyond procedures and paperwork: we examine your environment, turn risks into priorities and guide the improvements. This is how Cyberwise approaches every project:
- Technical and organisationalWe look at your IT environment and your organisation together: configurations, network and cloud, linked to governance, policies and compliance.
- Every framework, one approachNIS2, the Dutch Cybersecurity Act, ISO/IEC 27001, CyberFundamentals or TISAX: we work with the framework that applies to your organisation.
- Clear for IT and managementFindings translated into risk, priority and concrete decisions, for every role.
- Demonstrable resultsWe focus on concrete deliverables and check that measures actually work, not just that the documents exist.
- Together with your IT partnerYour IT partner or IT team implements the technical measures. We assess, guide and verify.
- Ongoing follow-upWith periodic reviews, CISO as a Service and Cyberwise ISMS, your security level stays on track long after the programme ends.
Our core value
Advice that serves only your interests.
Our core value is independence. We don’t carry out technical implementations ourselves and we don’t compete with your IT partner. That’s how we can give honest, objective advice, with your interests first.
- 1Independent findingsFindings and recommendations are based on risks and proven effectiveness, free from vendor or sales interests.
- 2Free choice of IT partnerYour IT partner or IT team implements the technical measures. You choose who you work with.
- 3No hands-on implementationWe assess and guide, but we don’t sell hardware or carry out technical implementations in your IT environment.
02Services
From first insight to ongoing follow-up.
- 01
Security assessments & audits
Know where you stand.
An independent assessment of your organisation and IT environment – from configuration audits and network scans to a pentest where it makes sense.
Result: Findings in context. A roadmap with clear priorities.
More about Security assessments & audits → - 02
Compliance & governance
From requirements to practice.
We build policies, procedures, registers and evidence tailored to your organisation. Your management decides; we guide the process and verify the agreed results.
Result: Workable policies, clear ownership and demonstrable improvements.
More about Compliance & governance → - 03
Improvement & validation
Improvements you can prove.
We turn the roadmap into technical work packages and guide the improvements. Your IT team or IT partner implements the technical measures; Cyberwise validates the agreed outcome.
Result: An improvement plan that actually gets followed through.
More about Improvement & validation → - 04
CISO as a Service
Clear direction for your cybersecurity.
Experienced security advice for management, without hiring a full-time CISO. We bring risks, actions and decisions together in a regular follow-up cycle.
Result: Well-founded choices. A clear follow-up rhythm.
More about CISO as a Service → - 05
Awareness & training
People make the difference.
Phishing simulations, workshops and management training connect cybersecurity to everyday decisions. Employees learn to recognise and report threats; executives learn to assess risks.
Result: Learn, apply and adjust based on your own context.
More about Awareness & training →
Looking for the full overview? View all services.
03How can we help?
Does any of this sound familiar?
Not sure which question fits best? Let’s look at it together in an introductory call.
- 01
We need to comply with NIS2 or the Dutch Cybersecurity Act
We work out what the law means for you and draw up a concrete roadmap.
- 02
We want to work in line with ISO/IEC 27001
We build the ISMS in line with the standard and, if you wish, prepare you for certification.
- 03
We want to know how secure we really are
The Cyberwise Baseline gives you an independent assessment and a roadmap with clear priorities.
- 04
We want our security to be tested
With a security audit, we test your environment – up to and including a pentest where it makes sense.
- 05
We’re looking for ongoing support
Periodic reviews, CISO as a Service and training keep your security on track.
- 06
We want to manage our ISMS in one place
Cyberwise ISMS brings policies, risks, measures and evidence together in one place.
Result
ISO/IEC 27001:2022 · DNV
04In practice
Nymus: information security as a basis for growth.
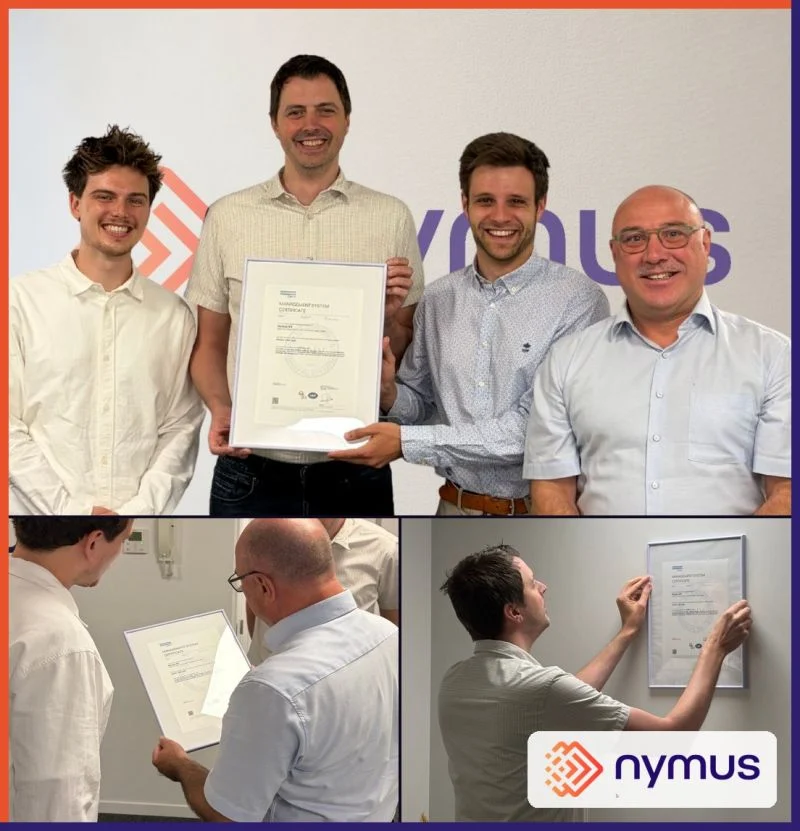
For e-invoicing partner Nymus, ISO/IEC 27001 was a deliberate step in its growth strategy. Larger customers expect demonstrable information security, and international growth brings additional requirements.
With guidance from Cyberwise, Nymus achieved ISO/IEC 27001:2022 certification from DNV: independent confirmation of its information security management system and a solid answer to customers’ security questions.
Read the case study05How we work
From analysis to lasting improvement.
Every broader programme starts with an independent assessment. We then guide the improvements and help keep your security level on track.
More about our approachServices under
AssessKnow where you stand
Audit, analysis and roadmap with the Cyberwise Baseline, including a gap analysis against your main standard or legal framework.
You get: Insight into which risks to tackle first and who is responsible for them.
View the Assess services →Services under
ImproveImprovements you can prove
Together with the people responsible in your organisation, we develop policies, procedures and registers and verify technical improvements.
You get: Workable policies, clear responsibilities and well-founded improvements.
View the Improve services →Services under
SustainOngoing follow-up
Periodic reviews, CISO as a Service, ISMS Document Care, training and Cyberwise ISMS.
You get: Regular reviews that make progress visible and flag new risks.
View the Sustain services →
06 / VLAIO · Flanders
Strengthen your cybersecurity with VLAIO support.
SMEs and social enterprises with a branch in Flanders can, under certain conditions, receive 50% funding for a cybersecurity improvement programme. We’ll look at which programme suits your situation.
- START
- 10working days
- MEDIUM
- 21working days
- PLUS
- 34working days
07Frameworks
One way of working. The right framework.
Each framework has its own scope and evidence requirements. In the introductory call, we determine which legislation, sector rules and customer requirements are relevant to you.
- BelgiumNIS2Belgian NIS2 ActFor essential and important entities in Belgium.
- NetherlandsCbwDutch Cybersecurity Act (Cbw)The Dutch implementation of NIS2.
- International27001ISO/IEC 27001Build an ISMS in line with the standard, with certification as a possible next step.
- AutomotiveTISAXTISAXInformation security in the automotive chain.
- EuropeCRACyber Resilience ActProduct requirements for products with digital elements.
08Cyberwise ISMS
Available in 2027
Your ISMS in one place.
A managed workspace that brings together policies, risks, measures, tasks, audits and evidence. We take care of set-up, operation and support; the content remains yours.
 Available in 2027
 DashboardTasks, quick actions, the ISMS assistant and key indicators in one overview.
 RoadmapActions with owner, deadline and status.
 Learning & AwarenessCourse and quiz per approved policy.
Sneak peek: we will show the final screens at launch.
09About us
The team behind your programme.
Roeland Vandekerkhove
Co-founder · ISO/IEC 27001 Senior Lead Auditor and DPO
Tom Hoogewijs
Co-founder · Microsoft 365 and Azure specialist
Stijn De Wilde
Cybersecurity Specialist
Nick Lievens
Trusted Advisor Cybersecurity & Compliance
Daphne Gérard
Project & Customer Success Manager

Your place in our team?
See our vacancies
10For IT partners
Independent cybersecurity expertise for your team and clients.
Cyberwise complements your knowledge of the client environment with independent security and compliance expertise. Our risk assessment and roadmap give you stronger backing for improvements and help the client make focused choices.
11 / Contact
Want to know where you stand?
Tell us what challenges you are facing. In a no-obligation introductory call, we look at what your organisation needs and what a sensible first step would be.